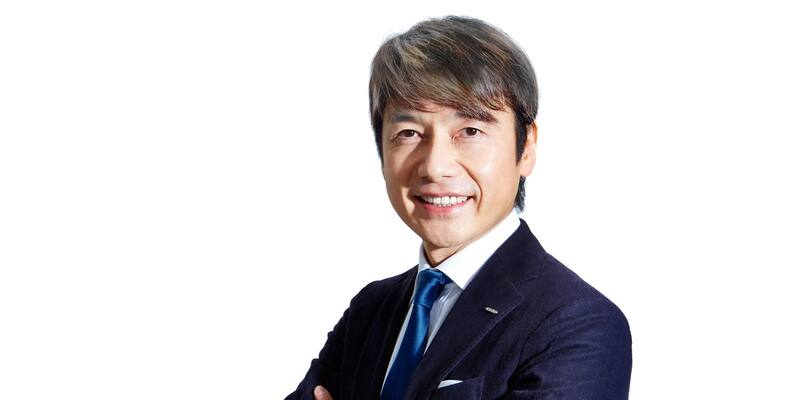
Masatoshi Kumagai, chairman and chief executive of GMO Internet Group, in an official company portrait. Image: GMO Internet Group (press release via PR TIMES)
The head of one of Japan’s biggest internet companies says AI has pushed the internet to breaking point. In a blog post on Sunday, Masatoshi Kumagai, chairman and chief executive of GMO Internet Group, wrote that “the internet itself is on the verge of breaking”, blamed the “explosive evolution and misuse” of AI, and urged Tokyo to turn its new active cyber defence powers on the people who attacked his company last week.
That attack hit Onamae.com Desktop Cloud, a GMO service that rents Windows servers to forex traders who run automated trading bots on MetaTrader. GMO says up to 26,739 servers may be affected, that customer information was taken, and that some customers found trades in their brokerage accounts that they never made. It began shutting every server at 4am Japan time on October 21 (19:00 UTC on October 20).
An “AI cyber saturation attack”
Kumagai, who founded GMO 31 years ago, says open-weight AI models have been stitched together into countless attack tools, so hacking that once took real skill is now open to anyone. As proof he points to ARTEX, an autonomous penetration-testing tool built for defenders, which GMO Cybersecurity by Ierae found running on the servers behind attacks on about 20 Japanese companies.
The same tool has been tied to break-ins at four South Korean banks and, by Microsoft, to a China-linked group that got into company clouds in under three hours. He also cites this month’s critical PHP flaws, which he says AI exploited within hours. As he put it:
We have already entered an era where, with only simple instructions, AI searches for weaknesses and drives itself all the way to a break-in.
Masatoshi Kumagai, GMO Internet Group, on his blog (translated from Japanese)
The result, he wrote, is an “AI cyber saturation attack”, in which countless AI-made attacks overwhelm defenders, and the raid on GMO is “the very symbol” of it.
What GMO hasn’t said
Neither Kumagai’s post nor GMO’s fourth incident report, published on Saturday, says AI was used in the attack on Desktop Cloud. ARTEX was found in attacks on other companies, not on GMO.
Kumagai also admits GMO had been warned. Its in-house white-hat hackers had flagged problems with the service, he wrote, but the team running it moved too slowly, “and attackers exploited that gap”. The attacker claims on a website of their own to have used weak settings, including one administrator account shared by every server, which GMO has not confirmed, ITmedia reports.
The attackers have demanded $50 million (about ¥8 billion), Kumagai said in a note added on Monday, and threatened more rogue trades on customer accounts at over 70 brokers, data leaks and ransomware. GMO says it will not pay. It will give every current customer ¥5,000 (about $30) and cover confirmed losses from unauthorised trades, even where a broker refuses a refund. GMO Internet Group shares fell sharply on Monday, Reuters reported.
“Not shifting our responsibility to the state”
On Saturday GMO asked the government to treat the case as the “first activation” of active cyber defence, which lets police and Japan’s Self-Defense Forces trace and neutralise attackers’ servers before damage spreads. The law took effect on October 1.
Critics were quick to point out that GMO is not one of the critical infrastructure operators the law is built around, and that the government, not a company, decides when to use it. Kumagai says he understands both points, and asks ministers to judge by the real effect on people’s lives rather than formal categories:
We are by no means shifting our own responsibility onto the state or pleading for a rescue.
Masatoshi Kumagai, on his blog (translated from Japanese)
Many users on X say he is recasting GMO’s own failures as a national problem, ITmedia reports. Kumagai says GMO will bear every cost itself and has 200 security staff on the case, using AI tools of its own to sift the evidence.
Tokyo steps in
On Monday Prime Minister Sanae Takaichi held the government’s first cabinet-level meeting on the wave of attacks and said that, once an attack is understood, Japan would “strategically choose and carry out every response option”, including neutralising attackers’ servers, the Yomiuri Shimbun reports. She ordered an emergency package of measures as soon as next week. Chief Cabinet Secretary Minoru Kihara has said any decision will rest on the law’s requirements, whatever GMO asks.
Update: attackers leak data, GMO offers a $1 million bounty
The attackers made good on a threat to publish customer data at noon Japan time on Tuesday, October 27 (03:00 UTC). GMO says it found what they claim is GMO and customer information online at 12:30 and is still checking it, warning that it may contain false material and that the leak site records the details of anyone who visits. It is preparing legal action against people who spread the data. The ransomware attack the attackers also threatened had not been seen by 13:55, and the customer computers GMO has examined so far showed no malware.
In its 12th report, GMO says it will “never” give in to the demands, since paying would fund crime and guarantee nothing. Customers whose data was published will get a special payment for each type of data exposed: ¥10,000 (about $65) for names and contact details, ¥15,000 for trading account logins and other financial or login data, and ¥25,000 for sensitive personal data, up to ¥3 million (about $20,000). That comes on top of the ¥5,000 payment and loss cover promised earlier. GMO is also setting up the GMO Cybercrime Bounty, worth up to $1 million in total, for information that helps police identify and arrest those involved, taking tips in Japanese, English and Chinese from noon Japan time on October 28. It says Trend Micro and several AI companies have offered help with the investigation.
Update: leak site taken down, 113 tips in six hours
The attackers’ leak site, mirrors included, went offline at about 04:00 Japan time on Wednesday, October 28 (19:00 UTC on Tuesday), when its domain was taken down after GMO worked with the companies involved, the firm said in its 13th report. It promises to move at once against any new site and warns that sharing links to the stolen data, or reposting it, could bring criminal complaints and damages claims.
The bounty site opened at noon Japan time and drew 113 tips in its first six hours, GMO said in its 14th report, which adds that it has sent 20 warnings over posts on X spreading the leak. It will publish the tip count every weekday until the attackers are arrested or put on an international wanted list. The customer computers it has examined still show no sign of malware or ransomware, and GMO asks customers to run a security scan and back up their files before switching their PCs back on.
Update: GMO says it has leads that could identify the attackers
GMO’s own team of white-hat hackers has found information it believes could lead to the attackers being identified, and is handing it to police and other authorities on Thursday, October 29, the company said in its 15th report, published at 12:40 Japan time (03:40 UTC). It did not say what the information is. The bounty site had received 270 tips by 11:30 that morning, up from 113 in its first six hours, and GMO repeats that it will take legal action, including criminal complaints, over the attack and the extortion. It asks people not to try to identify or contact the attackers themselves. In a stock exchange filing on October 28, GMO said its parent has found no other group service affected so far.
Update: Tokyo asks telecom firms to block the attackers’ site
Japan’s Ministry of Internal Affairs and Communications has asked private telecom carriers, through an industry association, to block access to a website believed to belong to the attackers, Jiji Press reported on Thursday, October 29, citing people familiar with the matter. It is a request, not an order, and the carriers have not said whether they have acted on it. Blocking is rare in Japan because carriers must look at where every user is connecting, which may breach the secrecy of communications guaranteed by Article 21 of the constitution; in July a panel advising the ministry said less intrusive options should be exhausted first. The leak site went offline on October 28, but a security firm told Jiji it was still partly viewable. Chief Cabinet Secretary Minoru Kihara would not confirm the request, saying only that the government has had various exchanges with carriers and would not discuss specific steps. GMO’s 16th report, published at 20:50 Japan time (11:50 UTC), says the bounty site had received 321 tips by 18:00 that day, 208 more than a day earlier, and that it will now publish the count every weekday at 18:00.
Update: GMO cuts its bosses’ pay
The boards of GMO Internet and its parent, GMO Internet Group, voted on November 2 to cut the pay of four executives over the attack, according to filings from both companies. Kumagai, who is paid as the group’s chief executive rather than by GMO Internet, loses 30% of his monthly pay for three months. GMO Internet’s president, Tadashi Ito, loses 25%, and executive vice presidents Hirofumi Yamashita and Kimihiro Kodama lose 20% each, starting with December’s pay. GMO Internet says the cuts reflect its assessment so far: it will now examine what happened before the attack and then reconsider where management responsibility lies. In a customer notice on October 30, it said it had begun contacting Desktop Cloud customers directly about claiming the compensation payments and the free replacement service it promised in its fourth report.
Update: Kumagai apologises and admits GMO ignored warnings
Kumagai and other GMO executives bowed repeatedly at the company’s first press conference since the attack, held in Tokyo on Monday, November 2, after the stock market closed, AP reported. “We’d like to apologize from the bottom of our hearts to customers and related parties who suffered damage,” he said, according to Jiji Press. He admitted the service had a security flaw: “It’s true that there was a security issue with our service,” he said, adding that experts had also told GMO about problems with the system. AP says he acknowledged the company had been warned internally about the weakness but failed to act, and that he apologised for recent social media posts, including a photo of himself smiling, that he said may have hurt victims’ feelings. GMO confirmed the attackers had deployed ransomware, AP reported, repeated that it will not pay, and said it would move to a new security system, compensate customers’ losses and pay every Desktop Cloud customer the ¥5,000 (about $33) goodwill payment it announced in October. Kumagai did not name the attackers, and nothing reported from the briefing says AI was used in the attack. GMO’s shares are down 17.5% this year.
Update: GMO begins contacting customers about trading losses
GMO Internet said on Friday, November 6, that it had started contacting customers one by one about compensation for losses from trades made without their consent through the hijacked Desktop Cloud service, the payout it first promised in its October 24 report. In a stock exchange disclosure the same day, it said it could not yet put a figure on the cost because neither the number of eligible customers nor the trades covered had been confirmed. It will give the latest claims figures, and an outlook for the hit to its results, at its earnings briefing on November 13.
Update: customers claim ¥3 billion in trading losses
By November 12, 2,943 FX accounts had claimed a combined ¥2.99 billion (about $20 million) for losses on trades the attackers placed, GMO Internet said in its third-quarter results presentation on Friday, November 13; the figure will be firmed up once GMO has checked each claim. Another 10,976 customers have applied for the flat ¥5,000 goodwill payment, worth ¥54.88 million so far (applications close on November 30, and the payments can reach ¥133 million at most). In all, GMO expects the direct cost of compensation to be about ¥3.05 billion (about $20 million), booked in the fourth quarter. It holds insurance that pays up to ¥1.1 billion (about $7 million), but says it does not yet know whether the policy applies.
Shutting Desktop Cloud is costing about ¥300 million (about $2 million) a quarter in lost sales and profit, and the investigation has cost ¥60 million so far, a sum it expects to rise. GMO has not changed its full-year forecast of ¥9.46 billion in operating profit because it cannot yet put a total on the cost, and says it will tell investors promptly if it expects a large hit. Its analysis of the cause, and measures to stop a repeat, will come later.
Why it matters
Kumagai runs one of Japan’s largest internet infrastructure groups, and his warning about cheap, self-driving AI attacks matches what security firms have found with ARTEX in Japan and Korea. But his own company’s breach followed warnings it did not act on in time, and nothing published so far shows AI was behind it.
Sources: Masatoshi Kumagai’s blog (October 25, updated October 26); GMO Internet, fourth report on the Desktop Cloud attack (October 24); GMO Internet, 10th to 12th reports (October 27); GMO Internet, 13th and 14th reports (October 28); GMO Internet, 15th report (October 29); GMO Internet, 16th report (October 29); GMO Internet, customer notice (October 30); GMO Internet and GMO Internet Group pay-cut disclosures (November 2); GMO Internet, compensation notice and disclosure (November 6); GMO Internet, third-quarter results presentation (November 13); AP (November 2); Jiji Press via Nippon.com (November 2); Jiji Press (October 29); ITmedia NEWS; Yomiuri Shimbun; Reuters via Newsweek Japan.
Latest Policy & Safety news