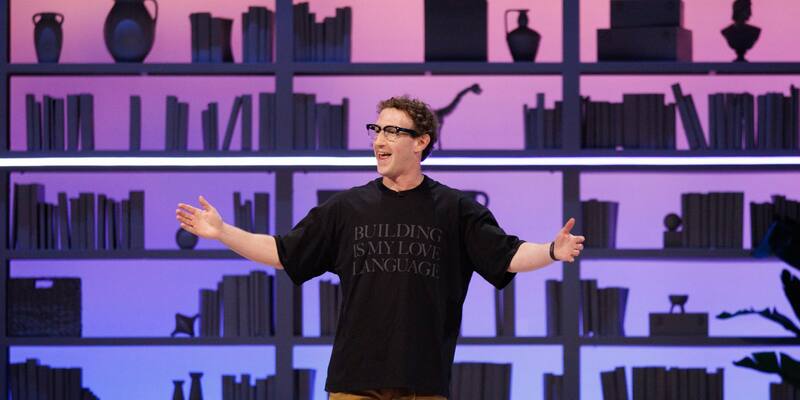
Meta CEO Mark Zuckerberg on stage at Meta Connect 2026 in September. Image: Meta
Meta’s Muse AI agent turns a shared conversation into a public web page, and security firm Claroc says those pages are far easier to find than users would expect. In a report published on October 18, its researchers say a single search of public DNS records turned up more than 6,800 Muse share links, some holding loan paperwork, a company’s internal revenue review and a job candidate’s notes for a confidential call with a frontier AI lab.
Claroc calls them GhostShares: pages that open for people who were never sent the link, and that those people can find on their own. Muse, which Meta has sold on its privacy design, launched on September 8.
How the links leak
Ask Muse to share a conversation and it publishes the chat as a page anyone with the link can open, with no login. Plenty of AI assistants work the same way. The difference, Claroc says, is in how Muse builds the address.
Each share gets its own subdomain under cf.metaaiusercontent.com, made from the conversation’s title followed by a random ID. Claroc’s simplified example: q3-revenue-review-7b1e42f0. The random part is long enough that nobody could guess it, but guessing is not needed: the first time anyone opens a share, their browser looks up the full hostname, and commercial passive-DNS services that watch those lookups record it and keep it searchable.
A month after launch, Claroc searched one such service for Muse’s domain and, after filtering out noise, got back more than 6,800 share hostnames, listed by title. “If you had asked us beforehand, we would have guessed that gathering these would take real effort,” the researchers wrote. “It took one query.”
Muse’s robots.txt file keeps search engines off share pages, avoiding the leak that put shared ChatGPT and Grok chats in Google results in 2025, but it does nothing to stop someone who already has the address. Claroc also found more than 75 saved scans of Muse shares on the public service urlscan.io.
What was in them
The researchers opened a few hundred pages, with no account. Most were harmless, but a minority were plainly sensitive. Claroc lists six by category, without names or links:
- a candidate’s prep notes for a confidential executive-search call with a frontier AI lab, naming the lab’s internal contact and the meeting time
- a national marketing company’s internal revenue review, marked for its CEO
- a small-business owner’s loan application, with the amount requested
- a to-do list including a bank fraud alert, with a partial account number
- a real-estate investor’s performance report, with two property addresses and mortgage figures
- a workplace’s full-year staff holiday calendar
Claroc says it has no evidence anyone has misused the pages, but warns that a list like this is “ready-made for fraud, impersonation or social engineering”. Muse was still creating new share hostnames when it last checked: 27 in a single day.
‘This behavior is by design’
Claroc says it reported the issue to Meta’s bug bounty programme on October 8. Asaf Aprozper, its co-founder and chief technology officer, told Ars Technica the company never heard back, and that it concluded Muse is working as Meta intended:
After checking similar platforms, consulting with industry colleagues, and re-reading Meta Muse documentation, we determined that this behavior is by design. However, users should be aware that when requesting Muse to share a chat with someone, it creates a public link that can be discovered using the passive-DNS techniques we described.
Asaf Aprozper, co-founder and CTO, Claroc
Meta has since paused sharing, changed the links and turned sharing back on (see the update below). Its help page for Meta AI share links warns that the links don’t expire and can be passed on.
It is Muse’s latest privacy and security problem: a user said the agent sold his keyboard and gave a stranger his home address, and Meta rushed to fix flaws that could have let users break into its internal systems before launch.
What Muse users can do
For now, the safest assumption is that any shared Muse chat is public: keep personal and work details out of conversations you plan to share, give them bland titles and delete share links once they have done their job. As Meta pushes Muse into workplaces, Claroc advises companies to find out which staff use it and, if they can’t monitor it, block muse.ai and metaaiusercontent.com on managed devices.
Update: Meta changes the links and turns sharing back on
Meta paused Muse sharing on October 20 after Ars Technica asked about Claroc’s findings. In a statement to Ars, it said it had “paused this functionality while we review this report and consider changes to how these links can be discovered”. When Claroc rechecked 40 shares that day, none of them opened.
Two days later, David Singleton of Meta Superintelligence Labs, Stripe’s former chief technology officer, said the problem was fixed and sharing was back on. He also took issue with how the flaw had been described:
An update on @Muse shared artifacts.
— David Singleton (@dps) October 22, 2026
Earlier this week, a security researcher published details of a design flaw in @Muse shared artifacts: some shared artifact URLs were discoverable via passive DNS. We disabled sharing immediately to prevent any unintended exposure, which is why shared artifacts were temporarily unavailable. Some articles we have seen in the press mentioned a flaw in chat sharing, and that is not the case - this issue was specifically about shared artifacts.
The underlying issue is now fixed, and sharing is back on.
If you shared an artifact before the fix: it now has a new URL. Anyone visiting the old link will see a note asking them to get the new one from you. We know that's a pain, and we're sorry for the disruption — but protecting user data has to come first.
We're grateful to the researchers who find and report issues like this. The Muse bug bounty program exists so these reports can reach us directly and responsibly, with awards of up to $300,000 for valid findings. Every report is reviewed. If you find something, please send it our way.
Muse’s help page describes artifacts as things such as documents, images, code and web apps that Muse can create. Claroc’s report calls the pages shared conversations, while Meta’s statement to Ars and Singleton’s post both speak of shared artifacts. Anything shared before the fix now has a new web address, and the old link shows a note asking visitors to get the new one from whoever sent it. Singleton didn’t say how the new addresses are built, and Claroc says the old hostnames, titles included, are still in passive-DNS history.
Singleton also pointed researchers to Muse’s bug bounty programme, which pays up to $300,000. Claroc says it reported the flaw there on October 8 and never heard back.
Why it matters
Muse asks for access to people’s accounts, documents and money on the promise that Meta can be trusted with them. A share feature that wrote the subject of private work into public records undercut that promise, and while Meta has now changed the links, the titles already logged can’t be taken back. In November, Claroc found the same weakness in apps built with Grok.
Sources: Claroc, “GhostShares”; Ars Technica (Claroc comment, Meta statement); David Singleton on X; Meta help page on artifacts.
Latest Meta news